
Delayed merge windows and broken build branches create a draining operational logjam that burns engineering velocity making specialized AI pull request review tools the most essential codebase asset for technical teams striving to sustain continuous integration speeds. When distributed software engineers commit multi directory script changes to a remote repository manual validation layers instantly become an administrative bottleneck. Code gatekeepers waste premium working hours reading raw text diff files instead of engineering macro application architecture. Transitioning your verification infrastructure toward autonomous inspection loops eliminates structural code latency before changes hit live staging paths.
To wipe out code merge backlogs and scale deployment speed engineering managers are abandoning static syntax formatting checkers. Integrating high performance AI pull request review tools into your Git workflow enables dynamic contextual logic auditing directly within active development branches.
These automated processing units parse incoming code logic identify deep security vulnerabilities and output exact optimization patches before a human reviewer opens the pull request thread. This proactive code tracking mechanism ensures clean source files while minimizing post deployment debugging cycles.
Deploying modern AI pull request review tools goes far beyond simple linter configuration choices. True pipeline optimization requires cognitive semantic engines capable of computing how a local function rewrite alters distributed database interactions across your entire software ecosystem.
Strategic Quality Management with AI Pull Request Review Tools
Modern application ecosystems require rapid iteration cycles to ship features without expanding internal system vulnerability windows. When product teams force large untested blocks of logic into main source trunks unexpected configuration stalls can rapidly cripple baseline web speed metrics. Manually tracing a memory leak or an unoptimized loop through a sprawling codebase after a deployment failure wastes valuable engineering output.
Utilizing an autonomous diagnostic framework such as automated root cause analysis allows technical leads to isolate structural compilation blocks before code packages are finalized.
Enforcing strict validation guardrails keeps web infrastructure stable when scaling customer transaction traffic. If an app runtime encounters a fatal serverless function timeout during peak usage spikes your operational interface experiences immediate response drops.
Resolving these complex software failures requires implementing advanced troubleshooting steps similar to an isolated vercel ai sdk error mitigation blueprint to maintain clean data streams across connected server setups.
The following table maps the core operational differences distinguishing standard rule-based linters from automated repository review networks.
| Evaluation Metrics | Standard Linting Checks | Agentic Review Implementations |
|---|---|---|
| Contextual Breadth | Scans local syntax structures line by line against fixed configurations. | Analyzes multi file dependencies and data flow patterns concurrently. |
| Vulnerability Isolation | Identifies basic formatting discrepancies or missing braces. | Catches semantic errors logical contradictions and API security leaks. |
| Actionable Remediation | Flags the breaking line location but requires human code correction. | Outputs clean traceable refactoring templates directly into Git strings. |
By shifting your repository gatekeeping away from legacy workflows you remove invisible bottlenecks before they degrade application efficiency. This modern verification approach preserves code architecture integrity as engineering velocity scales up.
For instance linking your branch analysis pipeline with comprehensive ai native software delivery lifecycle tools ensures that every functional release cycle adheres to rigid performance benchmarks without requiring slow manual code tracking sheets.
Architectural Blueprint for Integrating AI Pull Request Review Tools
Implementing an automated pipeline requires a systematic breakdown of the codebase evaluation journey. Software engineering directors avoid running unstructured loops that consume excessive inference compute tokens without returning precise telemetry. Deploying high-performance AI pull request review tools within continuous integration processes demands rigid operational boundaries. This metrics-driven strategy ensures that validation parameters remain objective and fully optimized across varying software repositories.
To establish a clean execution path development leads must categorize automated checkpoints into distinct functional layers. Isolating code changes within sandboxed testing frameworks allows the core engine to detect structural flaws before changes alter staging branch parameters. The following section blueprints the operational sequences required to configure a highly optimized review loop inside your version control environment using advanced AI pull request review tools.
Step 1: Code Branch Delta and Dependency Parsing
The initial phase isolates the exact code modifications submitted in the developer commit sequence. Tracking these early repository modifications ensures that external application files do not experience structural errors during the integration cycle.
- Analyze Incoming Code Changes: Inspect raw pull request diff strings to catalog altered line variables file path renames and structural configuration adjustments.
- Map Cross File Dependencies: Compute how changing an isolated logic module impacts imported functions and abstract class initializations in connected application directories.
- Validate Structural Formats: Verify that incoming source files pass baseline type checking parameters and syntax formatting criteria before running deep analytical checks.
Step 2: Contextual Threat Modeling and Security Gatekeeping
Securing the software network requires running targeted security checks immediately upon repository change detection. Advanced automated evaluation processes block systemic leaks before vulnerability windows reach public testing networks.
- Isolate Injection Vulnerabilities: Run algorithmic pattern matching scripts to locate unvalidated data inputs that expose application programming interfaces to malicious inputs.
- Scan for Hardcoded Credentials: Detect accidental inclusions of private encryption keys authorization tokens or backend database access strings before code updates merge.
- Enforce Regulatory Access Compliance: Cross reference the updated library packages with enterprise compliance frameworks to prevent introducing insecure third party software code.
Step 3: Algorithmic Logic Evaluation and Loop Optimization
The core computational analyzer inspects systemic code performance blocks to secure software operational integrity. Eliminating processing latency during the validation track guarantees reliable database interactions over high user concurrency periods.
- Identify Inefficient Nested Loops: Locate unoptimized data processing tracks that increase server computing cycles or trigger serverless function runtime timeouts.
- Detect Logical Contradictions: Flag conflicting conditional blocks that cause dead codes unreachable execution layers or invalid variable assignments.
- Verify Database Query Efficiency: Scan internal repository schemas to ensure database operations use indexed tracking pathways instead of triggering expensive full table sweeps.
Step 4: Automated Patch Generation and Remediation Output
Transforming complex code violations into clean executable scripts shortens internal refactoring windows. Delivering clear architectural reasoning directly to team developers ensures rapid system correction without manual engineering intervention.
- Structure Clean Refactoring Templates: Convert discovered logic bugs into precise readable code updates that match your team established naming conventions.
- Inject Inline Git Comments: Output the recommended optimization patches directly onto the breaking line coordinates within the active pull request dashboard.
- Provide Traceable Technical Reasoning: Detail the underlying operational explanation behind each suggestion so developers understand the performance gains immediately.
Step 5: Sandbox Verification and Merge Authorization
The final deployment checkpoint runs isolated compilation suite verifications to protect overall environment health. Recording comprehensive execution parameters guarantees that accepted code revisions operate flawlessly across digital server installations.
- Execute Isolated Workspace Builds: Compile the optimized branch inside a secure container to confirm the recommended patches resolve the original code errors cleanly.
- Run Regression Test Suites: Trigger automated verification workflows to guarantee that updating local files does not break global system stability variables.
- Log Performance Telemetry: Record execution speeds token consumption values and code health improvements inside your central software development platform dashboards.

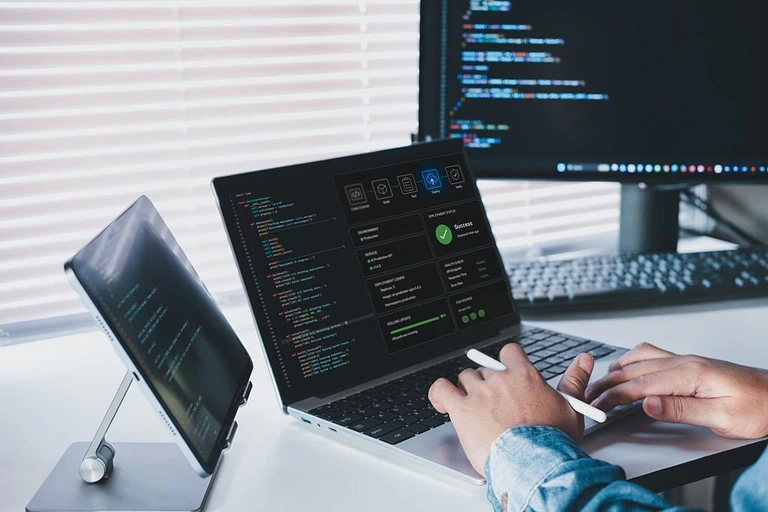
Tracking pipeline velocity metrics across active developer branches
Optimizing Code Reviews and Avoiding Automated Pitfalls
To extract the absolute highest return from repository automation development teams must look past basic automated comments and actively monitor review loop efficiencies. True system resilience relies on reducing pipeline friction while maintaining tight security gatekeeping parameters across every code branch. If your automated process outputs hundreds of vague alerts developers develop notification fatigue and ignore critical security suggestions.
Setting up an integrated tracking workspace similar to an ai agent observability system ensures that validation metrics remain clear traceable and actionable across all development pipelines.
Common Automated Code Review Mistakes
- Flooding Commits with Formatting Noise: Allowing automated systems to fill pull request threads with endless stylistic layout alerts masks major logical errors. Configure your engines to focus exclusively on architectural vulnerabilities and core runtime bugs.
- Omitting Local Architecture Context: Generic processing models evaluate changes in complete isolation without reading your external software directories. Provide deep vector indices to your tools so automated outputs respect your specific codebase dependencies.
- Granting Unchecked System Write Permissions: Allowing an autonomous script to merge high impact patches directly into main source trunks introduces immense operational risk. Always implement a strict validation layer that requires a senior team member to authorize final repository integrations.
If your pipeline lacks strict input data isolation a bad actor can exploit automated loops by injecting malicious code blocks into open source branches. Ensure your sandbox containers isolate external execution requests completely.
To accurately measure how effectively your development tracks are scaling evaluate these pipeline health parameters alongside basic comment volume statistics:
| Performance Identifier | Operational Definition | Strategic Engineering Value |
|---|---|---|
| Review Loop Velocity | The exact duration between a code branch commit and the automated patch feedback. | Shorter feedback loops remove merge backlogs and boost sprint speeds. |
| Patch Acceptance Rate | The percentage of automated review suggestions that team developers manually accept. | Measures output precision and filters out generic formatting noise. |
| False Positive Ratio | The proportion of flagged code violations that do not represent actual operational risks. | Low ratios prevent developer fatigue and preserve pipeline tracking integrity. |
| Sandbox Build Stability | The frequency with which recommended automated fixes successfully pass regression testing. | Guarantees that automated patch suggestions do not break global software systems. |
By coordinating your repository guardrails with this analytical blueprint you turn a basic code assistant into an indispensable security partner. Maintaining strict optimization metrics protects your software assets as feature complexity expands.
For deep dive validation structures across decentralized corporate environments check out the platform evaluation frameworks published by the AI Agent Evaluation Network to maintain strict quality metrics.
This metrics driven development framework guarantees that your platform achieves maximum delivery agility while keeping technical debt at zero.
To safely scale your infrastructure workflows you must align automation boundaries with authoritative cloud development principles. Software engineering teams can review the deployment rules outlined in the Microsoft Azure Architecture Framework to ensure distributed workloads remain secure.
Furthermore integrating your pipeline configurations with the development compliance models documented by the IBM Automation Center preserves operational security across enterprise grade software platforms.
Frequently Asked Questions
What is the difference between static code analysis and automated pull request reviews?
Static code analysis tools scan source files line by line against rigid rule configurations to locate basic formatting errors or syntax violations. Automated pull request reviews use cognitive processing engines to evaluate multi file dependencies track data flow patterns and comprehend human developer intent to provide working refactoring patches directly inside code branches.
How do automated review engines help software engineering teams lower operational risks?
These advanced tools perform deep contextual analysis across multiple directories simultaneously to catch structural errors logical contradictions memory leaks and unvalidated data entry loops during the initial compilation phase. This real time validation prevents bad code from passing to live production channels minimizing post deployment debugging overheads.
Can public repository automation systems leak our proprietary source code?
Yes if you use public open source extensions your input changes can be compiled into external model training datasets. To protect your intellectual property software enterprises must deploy secure enterprise grade platforms that guarantee absolute code isolation within sandboxed container environments.
When should an automated review process require a formal human checkpoint?
While low risk formatting fixes can run automatically high impact actions such as merging code to main source trunks altering private database permissions or updating financial transaction modules must always require formal human validation. Establishing mandatory human verification points blocks accidental security escalations.
How do automated programming tools handle structural schema drift?
Modern validation platforms execute deep sweeps across your entire codebase repository concurrently to locate deprecated syntax or breaking data models. The system highlights formatting shifts updates connection parameters and writes clean API integration layers autonomously to keep legacy environments stable as data structures evolve.