
Sharing a retail terminal or restaurant kiosk can quickly turn into a headache when workers are constantly locked out of their accounts, making the adoption of reliable passkeys for shared devices the smartest fix for modern business owners. In most shift-based workplaces, multiple employees use the same computer throughout the day, forcing them to type passwords dozens of times. To save time, people inevitably write passwords on sticky notes or stay logged into someone else’s account. Moving away from traditional passwords eliminates these frustrating delays and keeps your central company folders safe from accidental data leaks.
To speed up these daily logins and block security risks, smart business managers are trying a better approach. Using customized passkeys for shared devices allows a company to secure its public computers without making things difficult for the staff. Instead of memorizing a long password, an employee simply taps a small USB security key or uses a fingerprint scanner on the machine to sign in safely. This straightforward authentication method stops password theft entirely and keeps your daily business records highly accurate.
When setting up these passwordless keys on a public kiosk, the security token must belong to the physical device. The digital login details should stay locked inside the local machine instead of floating around on public web drives.
A Practical Approach to Kiosk Safety
Public computers need a clean login routine so shift changes do not slow down your daily business speed. When retail staff or warehouse teams rush through their duties on an unconfigured computer, mistakes can easily happen, causing important company files to go missing. Spending days tracking who made a specific change after a data breach wastes time and disrupts your operations. Building a clear preventative framework, like running a regular post quantum cryptography migration checklist, ensures your records stay completely safe before modern online scams can reach your system.
Setting up clear access rules protects your business profits as you upgrade your website and customer database software. If a multi-user platform allows employees to log into company drives using unprotected home networks, your business files remain vulnerable to external cyber attacks. Fixing these daily vulnerabilities requires a solid operational layout, similar to a well-planned digital transformation strategy, to ensure your business tracking stays clean and transparent.
The following table shows the practical differences between old-fashioned shared logins and modern passwordless security keys on shared computers.
| Workplace Setup | Old Shared Passwords | Modern Passwordless Keys |
|---|---|---|
| Who is Accountable? | Everyone uses the same text password, making it impossible to see who logged in. | Every employee has a separate key token, tracking actions accurately. |
| Scam Protection | Fake emails can easily trick workers into typing out the password. | Completely safe because there is no text password for hackers to steal. |
| Shift Handover | Accounts stay logged in for hours, allowing anyone to click your files. | The computer logs out automatically when a worker pulls their key out. |
By shifting your frontline security away from old typing routines, you remove dangerous blind spots before they can harm your central databases. This simple and modern update safeguards your business assets while helping your team complete their daily tasks much faster.
Setting up a passwordless routine on a busy workplace computer requires a clear step-by-step layout. Smart business operations leads avoid chaotic configuration paths that confuse the ground staff and cause constant technical support tickets. Using a standard SaaS onboarding checklist model during setup helps you plan every login boundary before distributing hardware keys to your team. Following a simple plan ensures that your kiosk security remains highly predictable, affordable, and fully optimized for daily retail or warehouse shifts.
To keep your workspace safe, you must break down the installation steps into independent, clear phases. Configuring your public hardware settings correctly prevents incoming employees from accidentally viewing sensitive company records left behind by previous workers. The following steps show exactly how to build a reliable security loop inside your computer network using customized passkeys for shared devices.
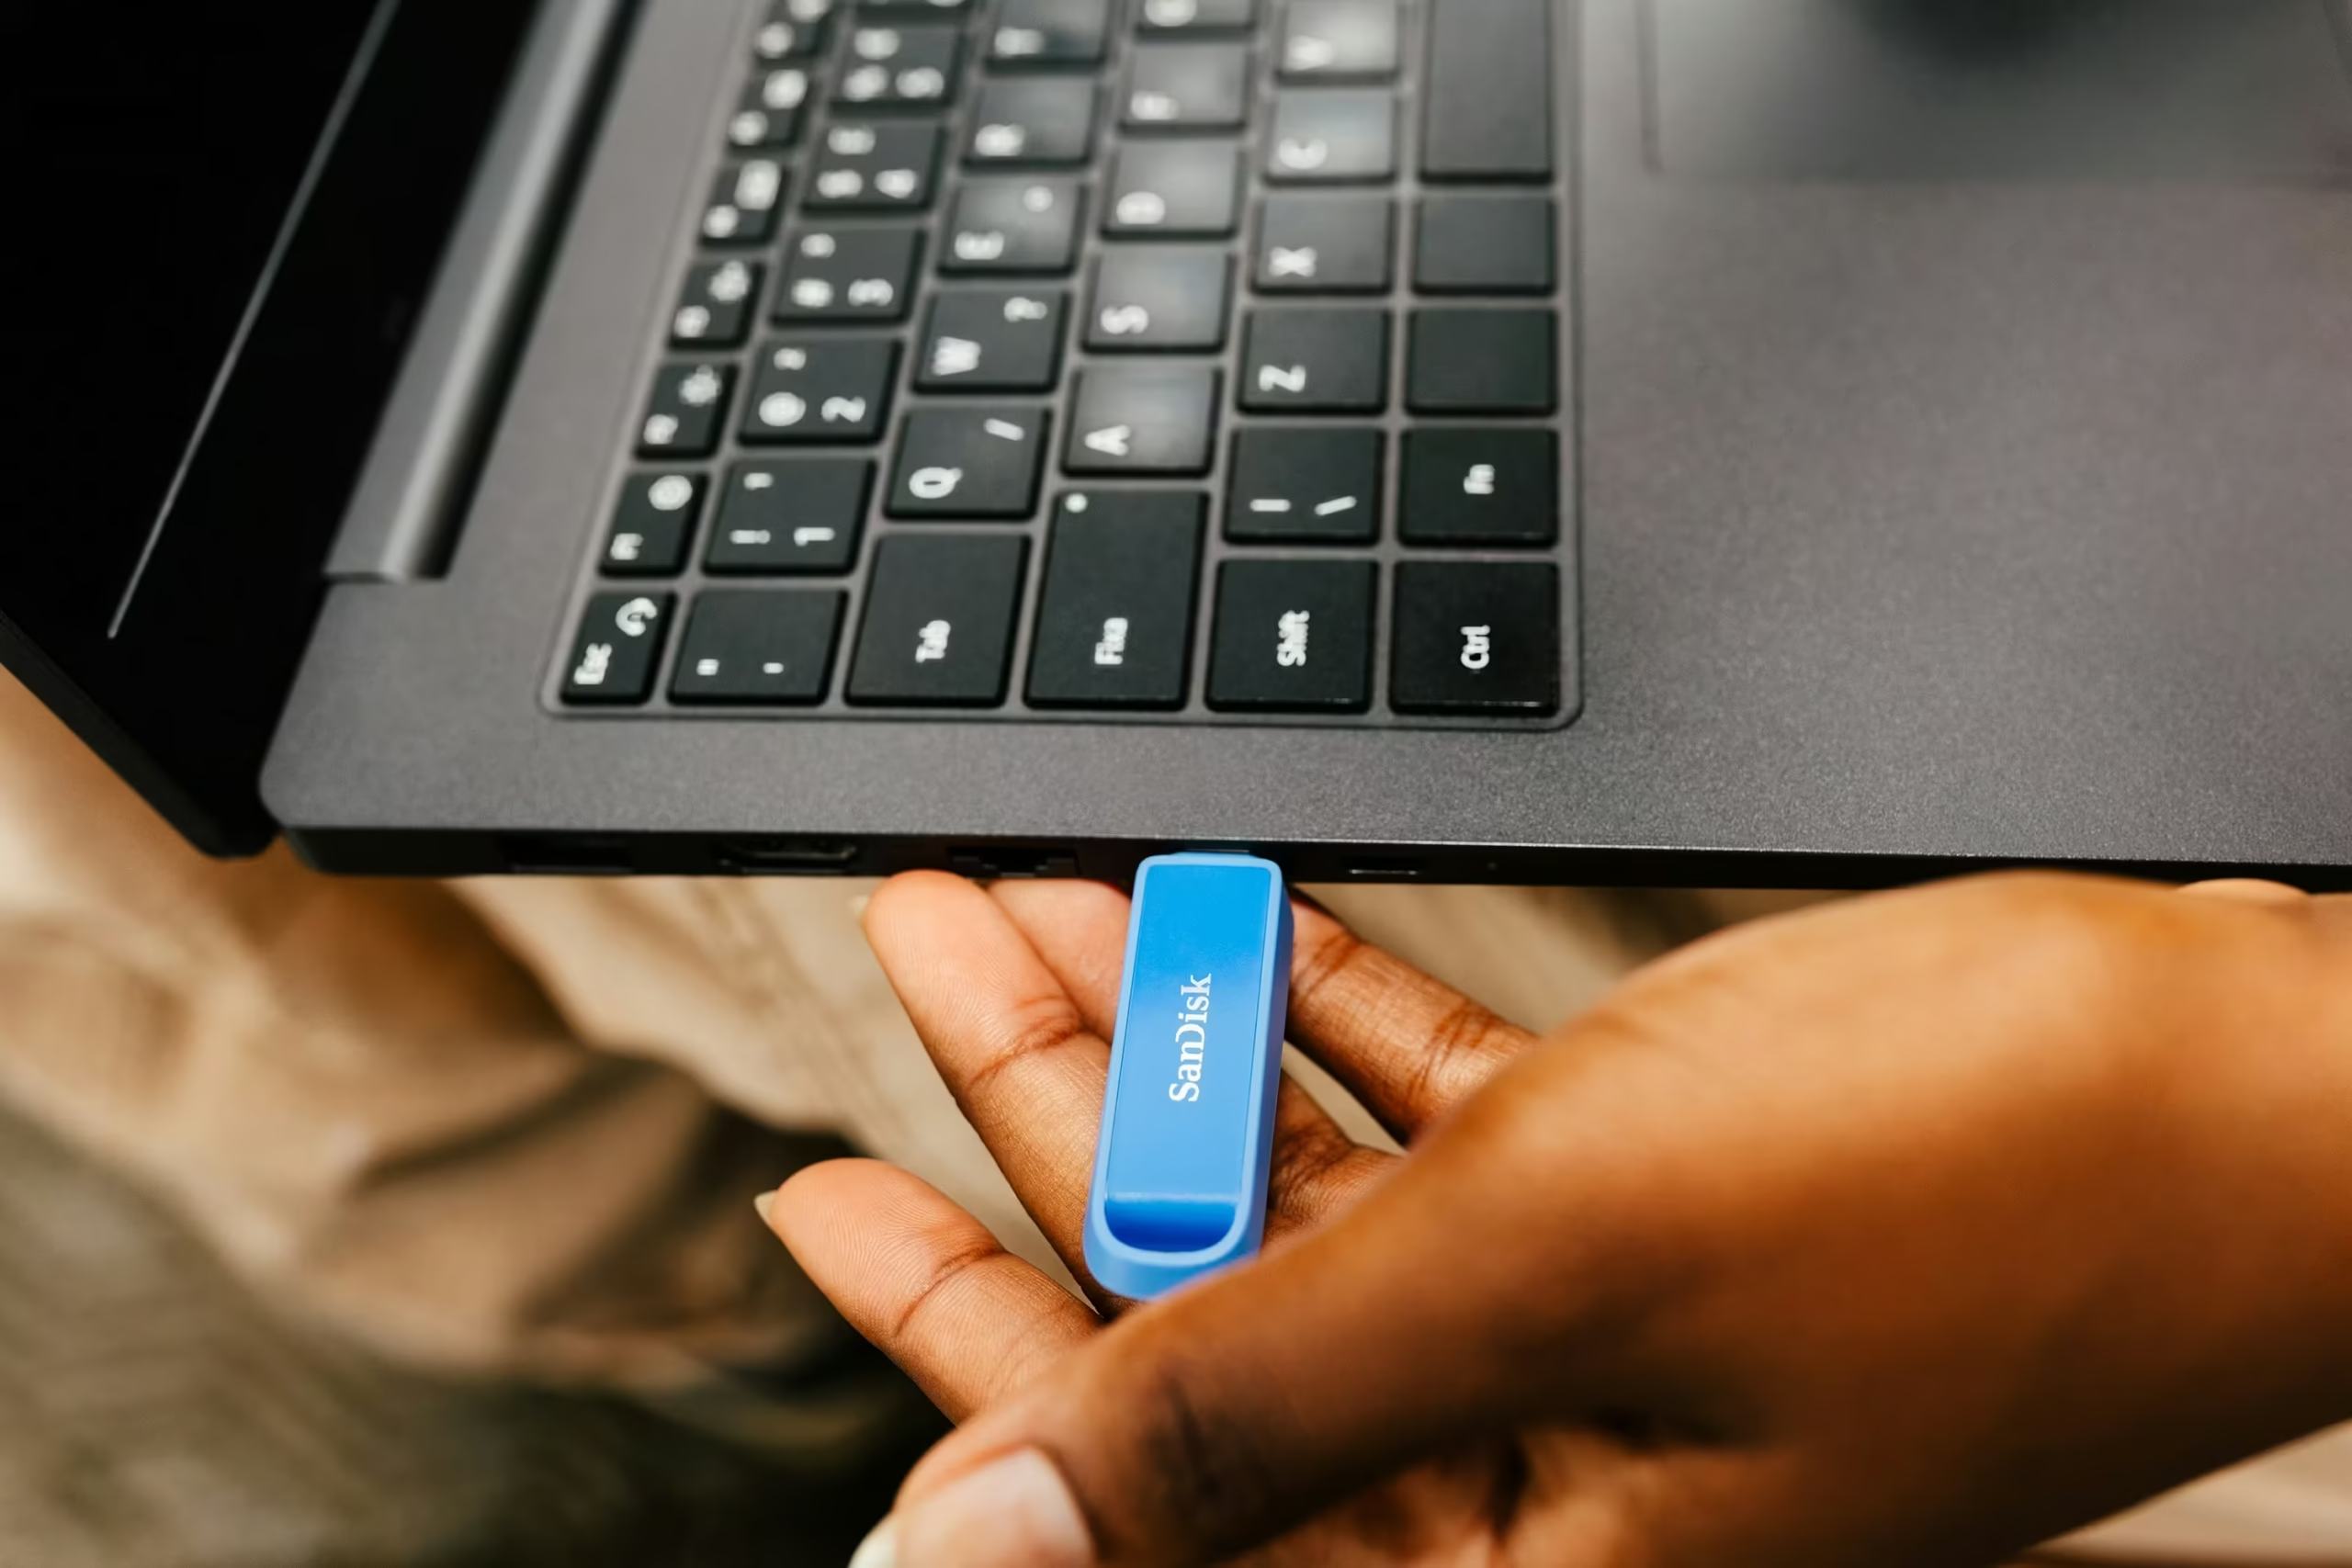
Step 1: Give Out Physical Security USB Keys
The first step focuses on selecting and distributing physical security tokens to your shift employees. Giving a separate hardware token to every single worker ensures that everyone can sign into public terminals safely without typing any text words.
- Check Your Public Computer Ports: Look at your retail kiosks or office laptops to verify they support USB or contactless card connections.
- Hand Out Individual Tokens: Provide a unique physical key to each team member instead of allowing staff to pass one token around.
- Set Up a Local Key Backup: Register a secondary master key for management so you can open a terminal if a worker misplaces their token.
Step 2: Turn On Automatic Sign Out Rules
Securing a public workstation requires making sure that old worker sessions close completely when their shift ends. Strict sign-out boundaries stop background files from staying visible to the next person who touches the screen.
- Activate Proximity Session Locks: Set the computer to lock or log out the exact second an employee pulls their USB key from the port.
- Set Short Idle Screen Timers: Configure the workstation to shut down active windows if the machine stays untouched for over two minutes.
- Turn Off Browser Form Auto Fill: Block your public internet browsers from remembering past typing notes or saving private employee text lines.
Step 3: Connect User Profiles to One Central Dashboard
An intelligent identity router handles individual access permissions to keep company files organized. Linking your local terminal handshakes to one central login hub ensures you can monitor employee entry metrics without slowing down retail checkout speeds.
- Build Simple Employee Groups: Categorize your workforce accounts by their actual duties so ground staff only see the folders they need.
- Link Each Key to One Name: Register every cryptographic key pair to a specific worker name to track changes accurately.
- Use a Single Sign On Service: Connect your public kiosks to your central office login software to handle database updates smoothly.
Step 4: Block Password Sharing Settings Completely
Restricting credential copying stops online scammers from stealing company login details through fake emails. Locking security codes directly inside the local computer hardware blocks human configuration mistakes from causing data leaks.
- Turn Off Password Creation Links: Prevent employees from creating or using old text passwords on shared workstations.
- Block Cloud Account Syncing: Turn off settings that automatically copy local terminal logins into personal consumer web drives.
- Restrict External Flash Drives: Lock your public computer USB ports so workers cannot download company files onto personal thumb drives.
Step 5: Run Weekly Security Audits
The final step focuses on tracking system access summaries to keep your corporate environment completely healthy. Reviewing your terminal usage patterns logs anomalies early before serious network perimeter violations can happen.
- Track Where and When Keys Are Used: Check your login dashboard weekly to see the exact time and machine name used by every employee.
- Flag Fast Multi Account Toggles: Set up an automatic alert if one machine registers multiple unique user logins within a few minutes.
- Update Your Device Software: Keep your terminal operating systems up to date so your passwordless hardware links always run flawlessly.
Managing passwordless access models on public workstations requires ongoing optimization to keep staff productive. If your identity system outputs vague error warnings during shift rotations frontline operators develop authentication fatigue and create risky workarounds to bypass security layers. A high false rejection rate forces team members to share physical resources or leave accounts permanently signed in on open kiosks.
Monitoring these performance patterns through a dedicated ai agent observability portal ensures that technical leads track login bottlenecks and terminal failures in real time.
- Flooding Terminals with Biometric Prompts: Requesting facial scans or fingerprint checks for minor software tasks disrupts active daily workflows. Configure your endpoints to lock down entry parameters only when an operator explicitly signs out or steps away.
- Ignoring Local Machine Context: Generic authentication rules evaluate login requests in isolation without reading hardware profiles. Provide specific configuration templates so setup tokens respect individual workstation limits.
- Granting Unchecked Root Write Access: Allowing public sessions to modify system registries inside core system directories exposes your business to malware threats. Always implement a hardware block that requires formal administrative clearance for configuration overrides.
If your corporate infrastructure lacks tight configuration guardrails an unattended kiosk can leave private data channels wide open to insider threats. Ensure your terminal triggers immediate session expiration loops the moment hardware keys are disconnected.
To accurately measure how effectively your digital workplace is scaling monitor these specific terminal metrics alongside basic entry statistics:
| Performance Identifier | Operational Definition | Strategic Engineering Value |
|---|---|---|
| Authentication Velocity | The exact duration between a physical token handshake and the secure account entry. | Shorter login timelines remove terminal queues and increase frontline sprint speeds. |
| Token Acceptance Rate | The percentage of cryptographic handshakes that public hardware stations successfully process. | Measures deployment precision and filters out conflicting interface signals. |
| False Rejection Ratio | The proportion of authorized employees blocked by localized biometric or proximity errors. | Low ratios prevent employee fatigue and preserve daily operational efficiency metrics. |
| Sandbox Environment Stability | The frequency with which isolated multi tenant sessions successfully clear historical cached data. | Guarantees that rapid shift rotations do not leak corporate data variables. |
By coordinating your public terminal perimeters with this metrics-driven layout you turn hardware keys into an asset. Tracking active user variables helps you assess credential risk when adding third party software apps. Review the analytical testing guidelines detailed by the AI Agent Evaluation Network to keep your identity health scores balanced.
To safely scale your system environments you must align passwordless access boundaries with enterprise grade hardware specifications. Technical teams can review the official deployment guidelines published on Microsoft Learn to ensure public workstations remain secure.
Furthermore integrating your system parameters with open source token rules keeps cross user operations highly stable. Reviewing the frontline research and identity deployment frameworks managed by the FIDO Alliance allows founders to prevent operational data drift across shared retail storefronts.
Frequently Asked Questions
Standard passkeys copy private cryptographic keys across cloud accounts to sync identities across personal devices like smartphones and single-user laptops. Secure passkeys for shared devices use non-exportable hardware bindings or secure security keys that lock the credentials to the local workstation preventing the key strings from syncing or leaving the terminal.
How do hardware authenticators prevent internal data leakage across distributed kiosks?
These advanced tools perform deep cryptographic handshakes that link user accounts to unique public key pairs. Because individual logins are tied directly to distinct hardware tokens instead of a single shared password bad actors cannot guess credentials or execute untraceable lateral movements inside corporate databases.
No sharing physical authenticators destroys individual accountability and makes tracking user modifications impossible. Every frontline operator must receive an individual token that verifies their unique identity parameters ensuring all database changes remain completely traceable in central server logs.
While low risk routine tasks can authenticate automatically via standard passkeys high impact operations such as changing master database access tiers exporting private customer lists or altering billing parameters must always require formal administrative authorization. These validation checkpoints stop privilege escalations.
How do hardware backed logins handle corporate data sync changes during fast shift handovers?
Modern validation platforms use automated system sweeps that clear temporary browser sessions instantly upon key disconnection. The terminal resets to a clean sandbox state while individual authentication channels remain synchronized with core access logs ensuring zero cross user data drift.